
BRONSCODE B.V.
Information security
A systematic and risk-based approach.
Bronscode B.V. takes a systematic and risk-based approach to information security, supported by an Information Security Management System (ISMS). This approach is inspired by the international standard ISO/IEC 27001 and aligns with the SURFaudit Assessment Framework.
Bronscode B.V. is ISO 27001 certified. You can download our certificates on the Certificates page.
Policy structure
Our approach is set out in a three-level policy structure.
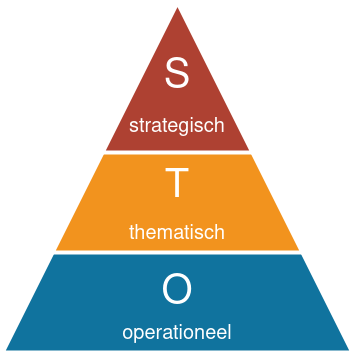
1. Strategic policy
The strategic information security policy describes the principles, scope and objectives of information security within Bronscode. It forms the overarching framework for the underlying policy layers.
Download the Information Security Policy v1.1.0 (Dutch)
2. Thematic policy
The thematic layer consists of specific policy documents (TSPs, Topic Specific Policies) that elaborate on topics such as incident handling, access management and continuity planning. They provide direction for processes, responsibilities and control measures. The following TSPs are available on request:
- TSP Incident Management
- TSP Business Continuity
- TSP Data Backup, Document and Information Control
- TSP Logging and Monitoring
- TSP Change Management
- TSP Identity and Access Management
- TSP Risk Management
- TSP Asset Management
- TSP Continual Improvement
- TSP Governance
- TSP Configuration Management
- TSP Secret Management
3. Operational procedures
At the operational level, work instructions and technical measures have been developed that follow from the thematic policy. These procedures are applied daily and periodically evaluated for effectiveness, based on risk analyses, internal audits and change management, among other things.
For further explanation or to inspect specific policy documents, please get in touch .